


IoT devices do a lot of small writes, suffer from sudden power cut-offs, operate in extreme conditions, and even use low-quality or fake SD cards. All of this may speed up wear and corruption.
SD Card Corruption in IoT Devices: Why It Happens So Often and How to Design Around It
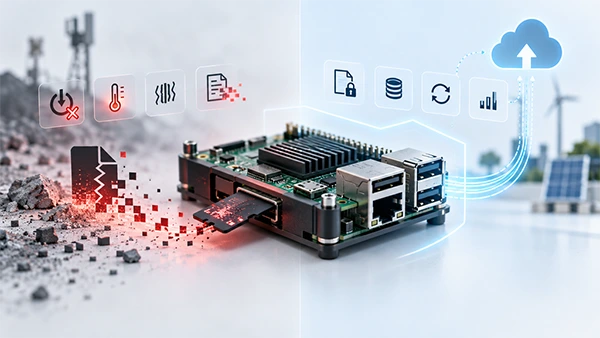
IoT devices can have good sensors, robust software, and an excellent housing, but all it takes is one small thing that can bring down the whole system – the SD card.
Storage problems can make devices fail to boot, cause data loss, and leave you without access to precious weeks and months of information. Unfortunately, all this happens in a predictable way.
Writing without stops, power outages, heat, vibrations, and low-quality flash memory generate conditions that consumer cards were never intended to withstand. This means that knowing about the possible issues can lead to a completely different approach to the matter.
Why IoT is the worst possible environment for an SD card
Consumer SD cards were designed for cameras and phones: occasional bursts of writes, gentle temperatures, a user who safely ejects. An IoT device violates every one of those assumptions.
- Constant small writes wear flash out fast. NAND flash cells tolerate a limited number of program/erase cycles. An IoT device logging sensor readings every few seconds, appending to system logs, and updating databases generates relentless small writes — and thanks to write amplification (the card must erase and rewrite whole blocks to change a few bytes), each tiny append costs far more wear than its size suggests. A card rated for years of photo storage can burn through its endurance in months of 24/7 logging.
- Power loss strikes mid-write. Most IoT devices have no graceful shutdown — power is simply cut when a battery dies, a breaker flips, or a user unplugs. If that happens during a write, the result ranges from one corrupted file to a mangled filesystem or, worse, interrupted internal card housekeeping that bricks the card entirely. Devices that reboot on a schedule or crash-loop multiply the dice rolls.
- The environment is hostile. Field-deployed devices bake in enclosures at temperatures consumer cards were never rated for, endure vibration in vehicles and machinery, and run for years without maintenance. Heat in particular accelerates flash wear and data retention loss.
- The card itself may be a lie. Counterfeit and low-grade cards are rampant in online marketplaces — cards that report 64 GB but physically contain 8, or that recycle rejected flash. In a phone, a fake card fails a user; in a deployed fleet, it fails a business.
If the card has already failed: recover before you reformat
When a device stops booting or its storage becomes unreadable, the instinct is to reformat and redeploy. Resist it — the data is often still recoverable, and the order of operations matters:
- Stop writing to the card immediately. Every additional write, including the device’s own boot attempts, can overwrite recoverable data. Pull the card and work on it from a computer.
- Image the card first. Create a full sector-by-sector image and run recovery against the copy, not the original — flaky cards degrade further with each read pass.
- Use recovery software before drastic measures. Logical corruption — damaged filesystem tables, deleted files, interrupted writes — is exactly what data recovery utilities are built for, and success rates on flash media are high when the card is still electronically alive.
- Escalate physically damaged or unrecognized cards. If the card no longer enumerates at all, the failure is likely at the controller or NAND level; that’s a job for a professional lab, not repeated reinsertion.
And once the data is back: treat the recovery not as the end of the incident but as the diagnostic. A corrupted card in an always-on device is a symptom of a design mismatch — which is fixable.
Designing devices that don’t eat their storage
Teams that ship commercial IoT products reliably converge on the same set of defenses — in fact, this checklist mirrors what Yalantis IoT consultants work through with device makers during a project’s discovery phase, when storage architecture and power-failure behavior are still cheap to change:
- Choose storage built for the duty cycle. Industrial-grade SD cards and eMMC modules use higher-endurance flash (SLC or pSLC instead of dense TLC), wider temperature ratings, and power-loss protection circuitry. They cost several times more per gigabyte and are worth every cent in a device you can’t easily reach.
- Make the operating system read-only. Mounting the root filesystem read-only — with a RAM-based overlay for temporary files — means the OS partition physically cannot corrupt on power loss. Many long-lived deployments boot read-only and confine all writes to one small, replaceable data partition.
- Buffer in RAM, write in batches. Instead of appending every reading the moment it arrives, accumulate data in memory and flush it in larger, aligned writes at intervals. This cuts write amplification dramatically and shrinks the window in which power loss can hurt.
- Use flash-aware, journaling filesystems. ext4 with journaling, or flash-oriented filesystems like F2FS, recover cleanly from interrupted writes far more often than legacy FAT — which, unfortunately, is still the default on many hobbyist images.
- Plan for power loss, don’t just hope. A supercapacitor or small battery that buys the device a few hundred milliseconds to finish writes and unmount cleanly eliminates the single biggest corruption trigger. Paired with a hardware watchdog, the device also recovers itself from hangs instead of crash-looping against its own storage.
- Don’t let the edge be the only copy. Sync data upward — to a gateway or cloud — on a schedule, with store-and-forward buffering for offline periods. Local storage should be a buffer, not an archive; once data is confirmed upstream, the card’s failure stops being a data-loss event at all.
The real fix happens before the first prototype
Notice that almost every defense above — storage grade, filesystem, partitioning, power design, data-sync architecture — is a decision made early in a product’s design, not a patch applied later. That’s the uncomfortable truth behind fleet-wide corruption problems: they’re usually architecture problems that were locked in before anyone thought hard about failure modes. Experienced device makers put storage reliability and data-loss risk assessment on the agenda before hardware is chosen, precisely because retrofitting endurance into a shipped fleet means recalls, truck rolls, and angry customers instead of a line item in a design review.
For teams already in the field with corruption-prone devices, the same checklist works in triage order: push data off-device more aggressively, switch the OS partition read-only in the next firmware update, and standardize on industrial cards at the next hardware revision.
Recover once, then design it out
SD card corruption in IoT devices isn’t random misfortune — it’s the predictable collision of consumer-grade storage with an always-on, power-unstable, unattended workload. When it strikes, disciplined recovery (stop writes, image the card, recover from the copy) will usually get your data back. But the lasting win comes from design: endurance-rated storage, read-only system partitions, batched writes, power-loss protection, and an architecture that never lets the memory card be the only place your data lives. Recover the card once — then build so you never have to again.
Frequently Asked Questions
Why do SD cards become corrupted in IoT devices?
What leads to SD card failure in always-on IoT devices?
Small writes, write amplification, unexpected writes caused by power cut-off, high temperature, vibration, and low-quality flash memory can all cause SD card failure.
Is it possible to retrieve data from an IoT SD card that is corrupted?
Yes, because if the card is still electrically accessible, then recovery software will be able to work with logical damage. Physical damage or unrecognized cards should be sent for professional data retrieval.
Related Posts
How Modern Enterprises Are Scaling Infrastructure with Custom AI
For many businesses, AI works as a collection of tiny experiments such as a chatbot, a coding assistant, or sometimes…
VMware vs. Sangfor aSV vs. Nutanix: Which Hypervisor Actually Saves You Money?
Selecting the right hypervisor isn’t simply an issue of technology; it could end up having a significant effect on your…
5 Best SaaS Platforms for Financial Services and Growing Businesses in 2026
In 2026, SaaS platforms have become essential for businesses that want to build smooth processes, automate routine tasks and clarify…
How Digital Records Support Workplace Injury Claims
An injury in the workplace does not necessarily mean that you have just a physical problem to overcome. It could…
What Happens When Your Office Emergency Plan Is a Drawer?
An office emergency plan should not end with the first aid box sitting in the last drawer. All employees should…
How Data Recovery and Recordkeeping Failures Cost Businesses More Than They Realize
Most businesses file data recovery issues and recordkeeping gaps under different headings, treating one as an IT problem and the…
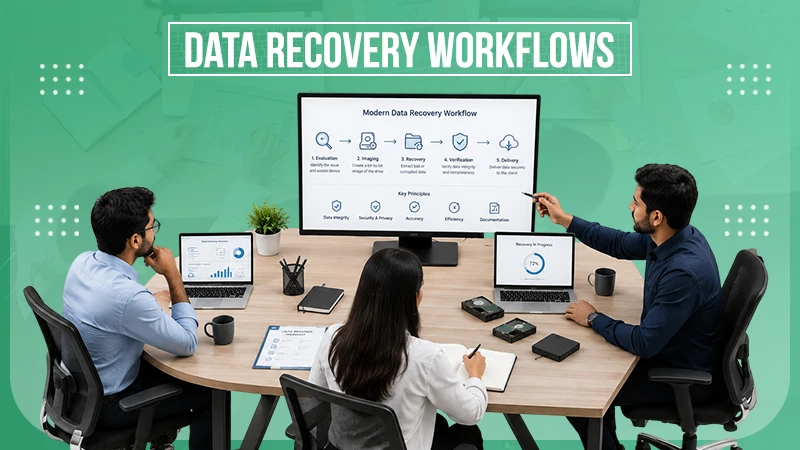
The Technical Skills Behind Modern Data Recovery Workflows
“The only truly secure system is one that is powered off, cast in a block of concrete and sealed in…
What is a RAID Array? RAID Levels Explained for NAS Storage
If you have recently bought a NAS or started looking for a better way to protect your files, you have…

Full vs Differential vs Incremental Backup: What’s the Difference?
Creating backups is easy, but choosing the right backup method is where most people get confused. Full, incremental, and differential…