


Ans. PAM is privileged access to authoritative access with credential controls, while identity management stores digital identity in which accounts and manages roles and rights given within boundaries.
Securing Sensitive Data Through Modern Privileged Access Management
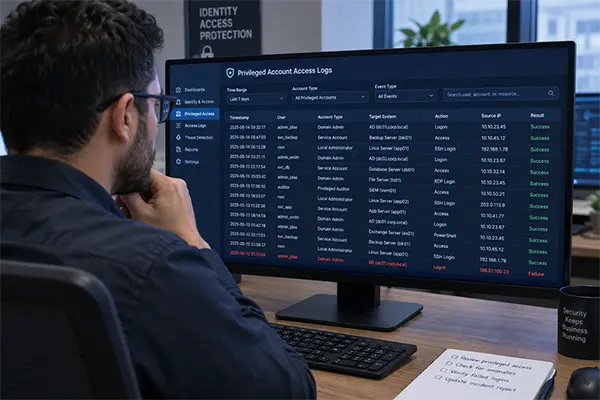
The initial traditional access management is far behind modern methods, as both have different security patterns for handling credentials. Security breaches are the one that officially improves the system from cybersecurity management, cloud servers, application logins, accounts details all have risk to expose with outer threats.
Some of the usual breaches are not from outside it always infiltrate through logins or inside server access. Whenever the situation occurs, it seems normal. These reports were found in Verizon’s 2026 Data Breach Investigation.
In this session, we tend to study what modern access management adds to the table where security parameters coincide. Also, what this brings forward with strong security firewalls in data breach incidents.
Why Credentials Became the Front Door
The numbers always tell the real picture behind this breach. A privileged system creates a bigger impact. It can access login info, create users, change security markup, install or download new applications, and access sensitive credentials.
The numbers found more interesting, recorded by DBIR in 2025, show that the most common breach is credential access at 22%, while attempts through vulnerabilities are 20%, and in most of the cases, around 88% of stolen details are used on web servers. Overall, recorded cases are 22,000, where 12,000 are confirmed breaches.
NIST explains that the best security for credential access in a system is to reduce availability among users to minimize threat attempts. Given that the task must be authenticated automatically before access.
Credentials create an opportunity when accessing multiple systems. These concerns raise higher to security risks, and Datarecovee’s data security and privacy resources provide a proper framework to focus on.
What Traditional PAM Actually Does
PAM has created more security parameters than before. It usually manages accounts where high risk is involved in the company profiles. Privileged accounts have credentials stored in vaults; users access the credentials and pull them back from vaults, then the passwords rotates with stores login credentials successfully.
This model also creates a responsive system. The management of admins is not required. This system is typically very helpful in investigations and measures the security level accurately. No further iteration to outer systems without management loosening controls.
More importantly, credentials are protected by system vaults; no one has direct access with it. Permission errors and administrator access give you authority to operate, while PAM operates at the enterprise level.
Where the Old Model Strains
There are four areas where to put pressure on the vault across old model principles. The pressure is extremely fatal:
- Infrastructure stopped sitting still. Dynamic identity frameworks work longer than static policies, which have a shorter span of a few minutes. An ephemeral compute system approach has weakened the system, whereas cryptographic hashing metadata with hostname still breathes.
- Machines started outnumbering people. They usually check workload access in the identity for CI/CD pipelines. Humans usually check login credentials manually, but the system doesn’t. Several accounts are accessed through the system without interference from code secrets that are in vaults securely.
- Privileged access moved into the browser. Access to systems where the admin’s important credentials are stored in cloud dashboards, with SSH keys on servers that are impossible to reach. These systems usually store the data in SaaS controls on servers.
- Third parties became part of the attack surface. Usually, most breaches recorded from outside the system architecture are basically third-party vendors, which also have access to privileged accounts stated by DBIR in 2025. These data is doubled with previous year’s reports.
What “Modern” Actually Means Here
Modern PAM adds value to a security credential more than traditional systems. The values are adaptive controls, cloud server integration, and personal verification. These changes give authority to task-oriented work only, accessed for a specific task.
Also added major security information: endpoint threats and cloud infrastructure are connected to the security protocol without administrative controls. These vault passwords are encrypted in cryptographic code, which rotates automatically every 15 minutes and is disabled afterward. No storage of credentials, only access personnel information. The threat is only about 15 minutes if leaked. This is hypothetical and not possible without server control access.
The vendor’s stake depends on BeyondTrust alternative, where they put themselves in a position that contradicts the arguments. They state that LDAP and Kerberos are not built for Kubernetes clusters and CI/CD pipelines, but the difference remains: cryptographic policies are always different from static servers.
How Organisations Should Evaluate This
The evaluation depends upon the limitations it carries and the process to find those system vulnerabilities.
- Ask what happens to machine identities. The modern approach, where server accounts and pipeline workflows face difficulties with hardcoded secrets compared to human interventions.
- Test the audit trail at the session level. Accounts that access and commands that follow have different recording directories, and this varies costs. Only login credentials are not enough for an audit trail; both records are beneficial.
- Check the break-glass path. Every system has emergency protocols; when used for high-severity incidents, they create an open risk aperture. Enquire about the protocols carefully, including system workflows and processes to control them.
- Count the integrations that already exist. Capture system-wide footprints that create the space. Cloud servers and consoles should be monitored in parallel, not shifted in any incidents.
- Establish what happens during an outage. If the access layer goes down, engineers still need to reach production. The answer to that question reveals more about a product than its feature matrix does.
Final Analysis
PAM is not the single factor that should be considered when securing system vaults. The traditional system has some values that can never fade: access control, credential vaults, session monitoring, and password modification. Modern PAM gives hard identity access, cloud servers, cryptographic coding, and automation of the system.
The main access for attackers is through privileged access to vendors or third-party integrations. This should be focused more on operations through system vaults. Several reports point to much higher integration than ever happened before. These values should be considered high protection through system management, proper backup facilities, protection through end users, and awareness about security protocols.
Datarecovee’s Backup Health Score Tools give access to testing, encryption, controls over log history, and recovery guidelines.
Frequently Asked Questions
What is the difference between PAM and identity management?
Does PAM stop credential theft?
Ans. Actually not. It usually lowers the risk exposed by time-limit guarantees not to reuse afterwards. A short span reduces the risk of theft more often.
Are service accounts covered by traditional PAM tools?
Ans. Traditional PAM tools and service accounts work differently in terms of coverage during deployment, while service accounts are handled with special care as their credentials are managed securely.
How does PAM relate to zero trust?
Ans. PAM usually covers the high-risk controls over a zero-trust system because zero trust more specially focus on user, location, and system behaviour. While PAM is one who manage the the system with authentication.
Sources
- Verizon Business — Additional 2025 DBIR research on credential stuffing
- Verizon Business — 2025 Data Breach Investigations Report, Executive Summary
Related Posts
How to Protect Business Data From Unwanted Scrapers
Scrapers are a well-known problem for businesses; protecting private records, discouraging unwanted bulk copying, and preserving access are topics one…
Your Email is Data Too: Testing AI Tools That Work Without an Account
People who read about data recovery are most likely to think hard about the place where the files can go.…
UX Design Firm or Full Product Partner: Who Owns the Outcome?
The ownership argument between both kinds of suppliers never ends. The sentence costs nothing to say, but blindly trusting that…
What is BitLocker and How Does It Work?
A stolen laptop can expose far more than the device itself. Your documents, work files, photos, and personal information may…
Beyond the Checkout: 5 Best High-Risk Merchant Account Providers for Online Businesses
Even with polished checkouts, online stores can still have trouble getting secure, suitable payments. The process is more complex than…
The 8 Best Automated Accessibility Testing Tools for Websites
Great copy and sharp design don’t prove that your website is accessible. It’s things like colour contrast, missing alt text,…
Cybersecurity Training for Beginners: 4 Practical Options Compared
Starting in cybersecurity is confusing because most beginner options look similar on the surface. Some are compact awareness courses, some…
The Ultimate Guide to Electronic Signatures for Businesses 2026
Electronic signatures are making modern workflows more convenient and time-saving. This guide to electronic signatures will let you know how…
How Email Authentication Fits Into a Layered Cybersecurity Strategy
One convincing email can be sufficient to pose major problems regarding security for a business. An email that appears to…